Canadian government websites taken offline after PHP vulnerability discovered
The Canadian Centre for Cyber Security and Statistics Canada were among the sites affected by the global security incident.
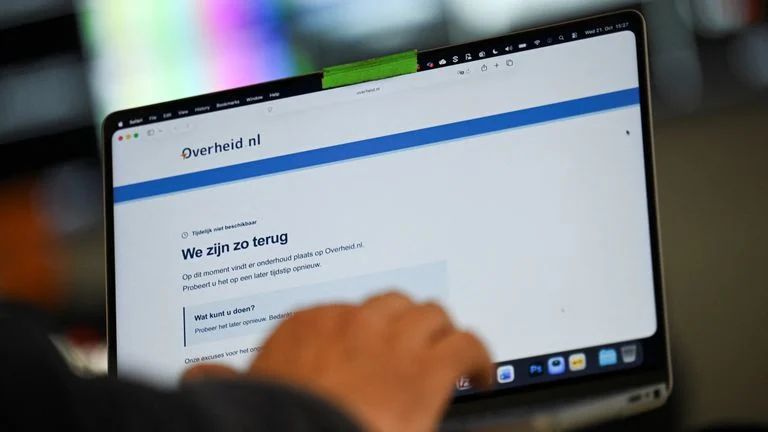
Numerous Canadian government websites were taken offline Wednesday to implement a security fix after vulnerabilities were found in PHP, a widely used programming language.
Artificial Intelligence Minister Evan Solomon said some federal government websites had been taken offline temporarily as a "precautionary measure," and urged organizations whose websites run on PHP to implement the security update.
"We are taking this situation extremely seriously," Solomon said in a post on social media. "The affected websites will be brought back online as soon as the fixes have been applied."
READ MORE: New Brunswick resident finds third data centre proposal in his neighbourhood
READ MORE: AI agents attempted to hack Canadian government website, researchers say
The websites for the Canadian Centre for Cyber Security and Statistics Canada appeared to be down for a period of time on Wednesday when CBC News attempted to access them.
Provincial sites for Newfoundland and Labrador and Prince Edward Island were also offline, displaying messages saying the shutdown was due to a global security incident.
PHP developers on Wednesday released urgent new fixes to vulnerabilities in their software, and encouraged website operators to implement the solution as soon as possible.
"If you run PHP, it is imperative that you update now," the PHP Foundation said in a news release.
PHP is a language that dates back to the early 1990s and initially stood for "Personal Home Page." It underpins huge parts of the public-facing web and is baked into sites like WordPress, Drupal, Joomla and Magento.
When a visitor loads a page that uses PHP, a server running the language assembles the content and sends it to the browser. It is free, open source software, maintained by volunteers.
PHP runs roughly 75 per cent of websites whose programming language can be identified, according to web technology tracker W3Techs.
"When it comes to PHP in particular, that is foundational to the internet," said Ritesh Kotak, a Toronto-based cybersecurity and tech analyst.
Because of that, he says many websites are vulnerable to hacks until the fix is implemented, making the scale of the situation "absolutely scary."
Kotak said that bigger companies and organizations with large IT teams will be able to implement the fix more quickly, but says medium or small ones will be vulnerable for longer or may struggle to implement the fix because they don't have the same resources.
In a blog post, Alphabet-owned cybersecurity company Wiz said it discovered the flaw in PHP using artificial intelligence.
The company said the vulnerable code had been present for more than a decade, and that they used multiple large language models to find the vulnerability and validate the patch for the problem while working with OpenAI on discovery and patching.
They also co-ordinated with Automattic, AWS, Microsoft and others on the rollout of the patch, so they could give guidance to customers that cannot implement the fix immediately.
PHP Foundation said a possible exploit for one of the vulnerabilities was first "theorized" in 2024, but the foundation explained to CBC News in an email that each of the solutions it came up with caused new problems.
A lack of resources and other issues taking precedence led to the delay in fixing the problem, according to PHP.
Kotak says while AI helped in this case to find the vulnerabilities and fix them, it can also be used by hackers to find those weak points and exploit them.
"With [AI], you could have thousands of hackers using the latest and greatest tools and knowledge that is out there going out and trying to get into systems and infiltrate databases," Kotak said.
For that reason, he expects to see more cybersecurity incidents in the future.
Elsewhere around the world, cybersecurity agencies in Europe, Australia, Japan and Britain also urged PHP users to make the fix, while governments in France, the Netherlands and other European countries proactively took their websites offline to make the fix.
With files from The Canadian Press, CBC News and Radio-Canada